Cookies Privacy
I accept Cookies Policy We use cookies to understand how you use our website and to improve your experience. By continuing to use this website, you accept our Link is copied!

PCI DSS Advisory

PCI DSS advisory services help organisations understand payment-data scope, assess control readiness and organise remediation before the applicable self-assessment or independent validation process. The service is intended for merchants, service providers and technology teams that store, process, transmit or can affect the security of payment account data.

Outcomes this service supports

This work turns compliance and risk ambiguity into fundable, evidenced, owned decisions.

  • Confirm the cardholder-data environment and connected-to scope.
  • Identify opportunities to reduce scope safely.
  • Assess control and evidence readiness.
  • Prioritise technical and procedural remediation.
  • Prepare responsible teams for the applicable validation route.

What we cover and produce?

We agree the precise scope up front. Depending on the objective, environment and authorised access, the engagement may cover:

  • Payment flows, systems, people, locations and third parties.
  • Network segmentation and scope validation.
  • Secure configuration, vulnerability management and testing.
  • Access control, authentication and logging.
  • Protection of stored and transmitted account data.
  • Policies, incident response, monitoring and evidence.
  • Service-provider responsibilities and shared controls.
  • Readiness for SAQ, ROC, ASV scans or penetration-testing dependencies as applicable.

How delivery is structured?

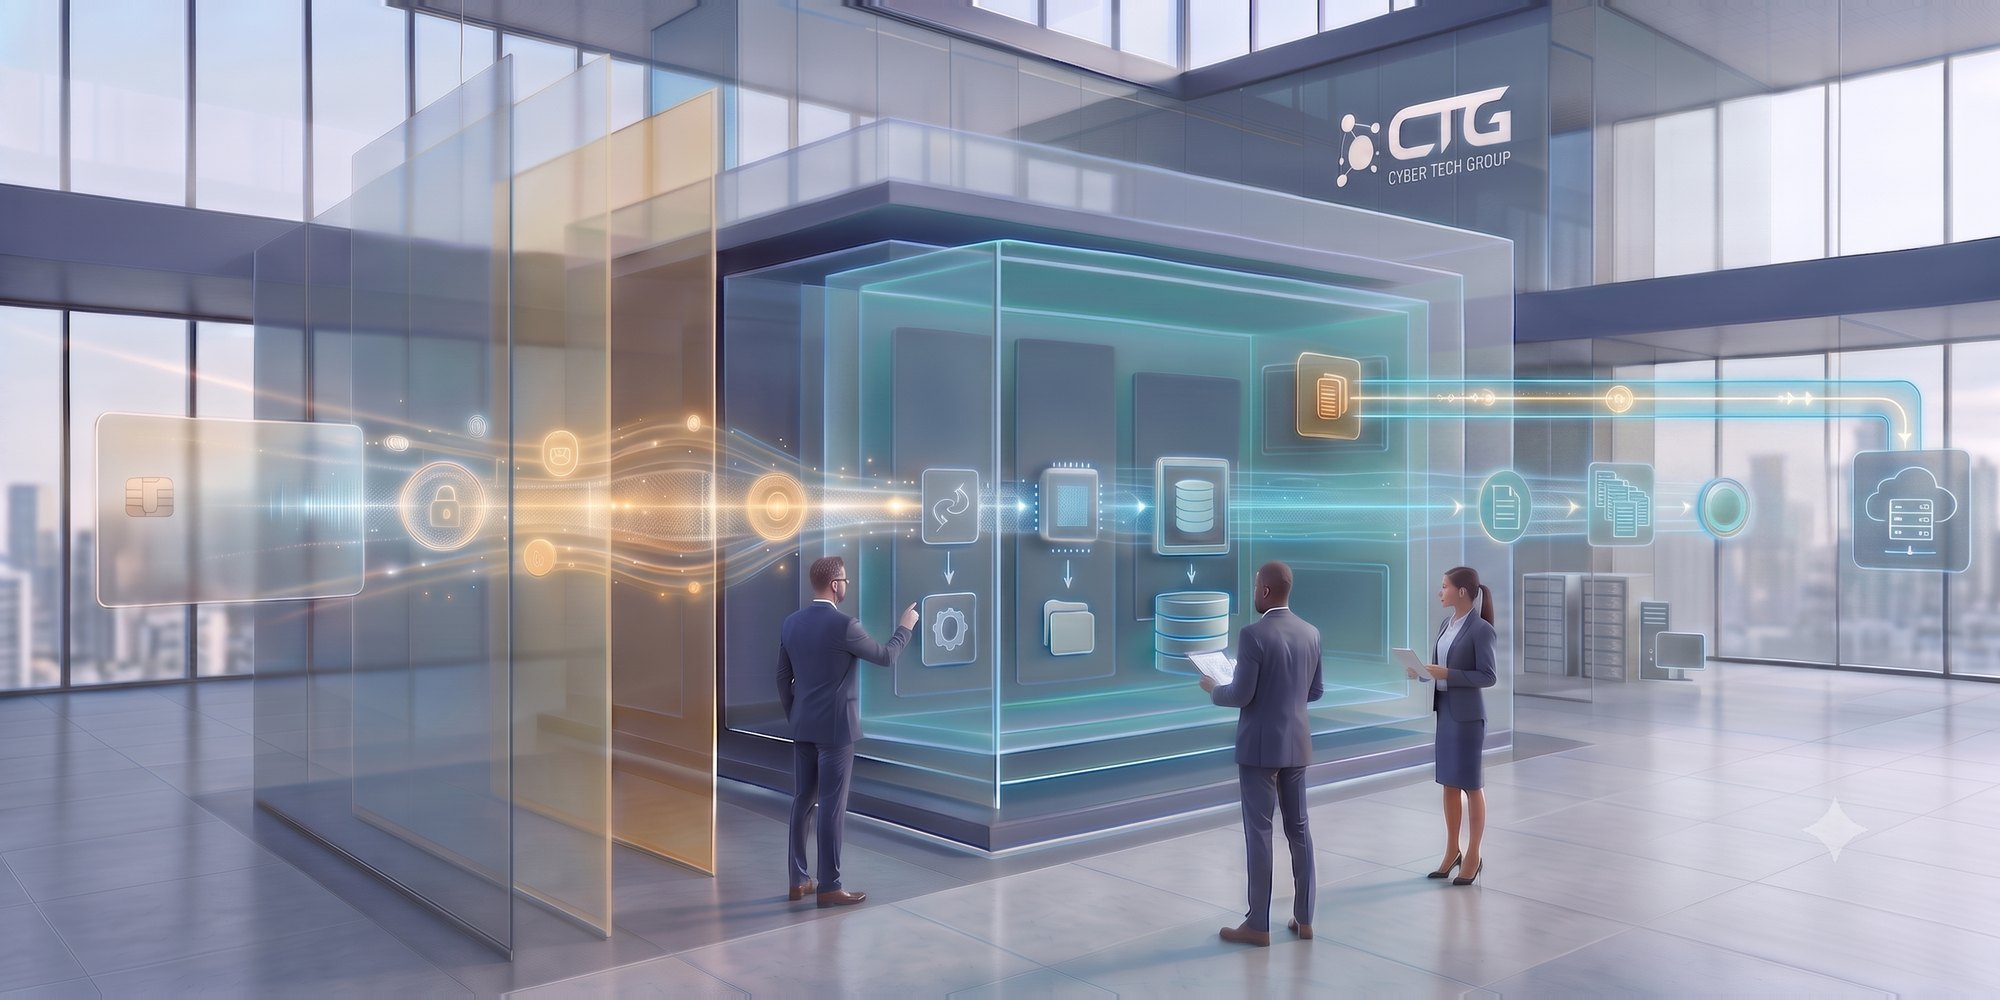
Document how account data enters, moves through and leaves the environment.

1. Map payment-data flows:

Identify in-scope components, connected systems, service providers and opportunities for validated scope reduction.

2. Confirm scope and responsibilities:

Review design, implementation and operating evidence against applicable requirements.

3. Assess control readiness:

Prioritise gaps and coordinate technical testing or evidence preparation.

4. Remediate and validate:

Support the customer’s SAQ or engagement with the appropriate assessor without overstating CTG’s role.

5. Prepare the validation package:

What you receive?

Outputs are prepared for executives and for the technical teams doing the remediation. Depending on scope, they may include:

  • Payment-data flow and scope map.
  • PCI DSS gap assessment.
  • Segmentation and scope observations.
  • Prioritised remediation plan.
  • Evidence and responsibility matrix.
  • Technical-testing coordination plan.
  • Validation-readiness summary.

How we keep the work controlled?

CTG confirms the decision to be supported, the evidence threshold, responsible stakeholders and the distinction between advisory work, implementation, legal interpretation and independent assurance. Findings are linked to owners, dependencies and measurable next actions.

Typical triggers for this work

  • Payment environments have changed.
  • A merchant is uncertain which SAQ applies.
  • A service provider must prepare for customer assurance.
  • Scope is larger than expected and segmentation needs review.
  • Recurring ASV, penetration-testing or evidence failures occur.
  • The organisation is preparing for a QSA-led assessment.

Frameworks, scheduling and scope limits

The engagement may draw on PCI DSS current version, PCI SSC official guidance, applicable SAQ and testing requirements. Where we cite a standard, it explains our method only - it is not a certification, accreditation or official determination.


We confirm the timeline at scoping; it reflects the environment's complexity, the evidence on hand and access to the right people.


CTG must not imply Qualified Security Assessor or Approved Scanning Vendor status unless current evidence confirms it. Final validation requirements and assessor acceptance depend on the organisation’s role, acquiring arrangements and applicable PCI SSC programme rules.

Discuss PCI DSS Advisory with CTG. In a focused scoping call we agree the objective, scope, evidence, delivery model and outputs, then send a proposal.

Related services

Frequently asked questions

What does PCI DSS Advisory cover?

We agree the precise scope up front. Typical areas include payment flows, systems, people, locations and third parties, Network segmentation and scope validation, Secure configuration, vulnerability management and testing, and Access control, authentication and logging. The proposal documents what is out of scope, what access we need, what you provide and how success is judged.

What will we receive at the end of the engagement?

Deliverables depend on the agreed objective and may include payment-data flow and scope map, PCI DSS gap assessment, Segmentation and scope observations, and Prioritised remediation plan. We connect each key conclusion to its evidence, its impact, its priority and an accountable action.

What evidence should we prepare?

CTG normally requests the policies, registers, governance records, technical evidence and previous assessments relevant to the agreed scope. The evidence request is tailored so that the customer does not collect material that will not be used.

Does this service provide legal advice or certification?

No. CTG provides cybersecurity assessment and implementation support within the agreed scope. Formal legal interpretation, statutory assurance and accredited certification remain separate.

How long does the engagement take?

We confirm the timeline at scoping; it reflects the environment's complexity, the evidence on hand and access to the right people.

How does this relate to External and Internal Penetration Testing?

They address adjacent but separate needs. Scoping identifies whether PCI DSS Advisory, External and Internal Penetration Testing, or a coordinated programme is the smallest useful approach without duplicating work.

What are the principal limitations?

CTG must not imply Qualified Security Assessor or Approved Scanning Vendor status unless current evidence confirms it. Final validation requirements and assessor acceptance depend on the organisation’s role, acquiring arrangements and applicable PCI SSC programme rules.